KPMG CTF 2026 Campus Edition
Writeups for KPMG India's Cyber Threat Flag 2026 Campus Edition, a 48-hour jeopardy CTF I played solo, covering Web, API, AI/LLM, infrastructure, reverse engineering, mobile, cryptography, OSINT and OT/IoT challenges.
Final results are announced on Oct 19, 2026
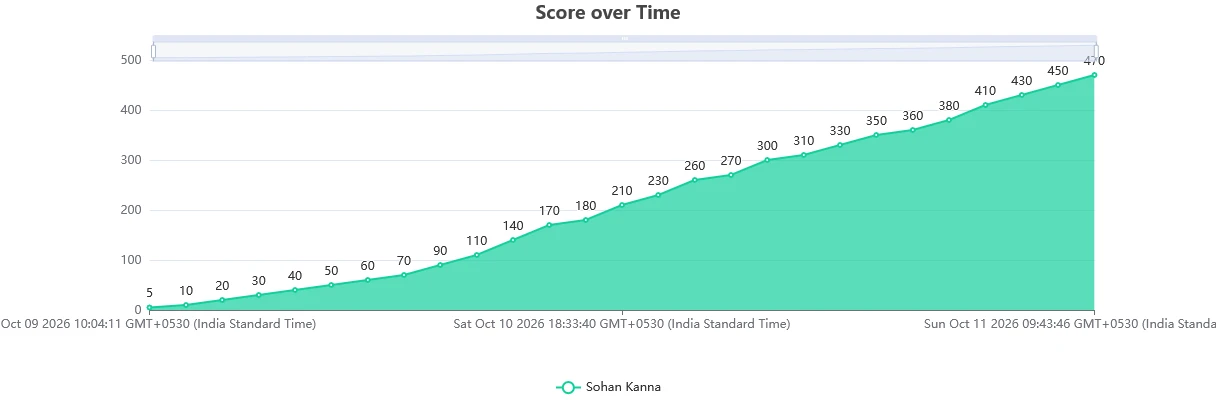
KPMG India's Cyber Threat Flag 2026 Campus Edition ran for 48 hours, from October 9 to October 11, 2026. I played it solo and finished with 470 points.
The challenges spanned almost every corner of offensive security: LLM assistants that leak data or can be talked into SSRF, GraphQL and MCP-backed APIs, weak infrastructure, an MBA-obfuscated bytecode VM, an Android app, PLC and MQTT devices, and multi-hop OSINT trails.
Each writeup walks through how I approached the challenge, not just the final payload: what the description was hinting at, what I tried, and why the solution works. They're grouped by category below, easiest first.
Challenges
AI / LLM
3 challenges · 40 pts- 10 ptsAcmeBank AssistantA broken-access-control (IDOR-style) prompt injection: AcmeBank’s support assistant trusts a user-supplied account identifier with no authentication, so simply claiming userid = admin makes it hand over the restricted admin account record in KPMG CTF 2026 Campus Edition.3 minEasy
- 10 ptsSecureBot SupportWalking through a prompt-injection challenge against an LLM support bot guarding a secret: why the obvious jailbreaks (base64 smuggling, “ignore your instructions,” authority role-play) all failed, and how a plain request to dump the system prompt as JSON leaked the master access code in KPMG CTF 2026 Campus Edition.5 minMedium
- 20 ptsWebSummarizer ProAn agentic SSRF challenge in KPMG CTF 2026 Campus Edition: the LLM summarizer blocks the cloud-metadata IP by string, but validates on the raw text rather than the normalized address, so encoding 169.254.169.254 as its decimal integer form slips past the filter and reaches the protected /health endpoint holding the flag.4 minMedium
API
3 challenges · 60 pts- 20 ptsArclight 1A GraphQL excessive-data-exposure challenge in KPMG CTF 2026 Campus Edition. The dashboard only ever requests id, username, email, but the User type also carries a hidden flag field. Introspection is blocked by role, yet type-specific introspection still works, revealing the field and letting an ordinary user read the admin’s flag the UI never asked for.3 minEasy
- 20 ptsNexus APIHow I chained a leaky “debug” config endpoint and a stupid duplicate-slash route to forge my way to root command execution on NexusAPI — KPMG CTF 2026 Campus Edition.3 minMedium
- 20 ptsTradeBotA race-condition challenge in KPMG CTF 2026 Campus Edition against an MCP-based trading API. The settlement engine checks admission before routing finishes and never re-checks, so firing a burst of concurrent orders violates settlement exclusivity (SETTLEMENT_OVERSUBSCRIPTION) and the reconciliation path leaks the sealed reserve-vault record holding the flag.4 minMedium
Cryptography
2 challenges · 40 pts- 10 ptsOnionPeeling back four layers of an “onion”: binary, Base64 and hex encoding, then an Atbash cipher, to recover the flag from a 10-point crypto challenge in KPMG CTF 2026 Campus Edition.3 minEasy
- 30 ptsCorrupted VisionA three-layer forensics challenge in KPMG CTF 2026 Campus Edition: repair a JPEG whose magic bytes were overwritten with a PNG signature, lift the SOF0 height to un-crop hidden rows of the image, then decode a null cipher where each word’s length (3/5/7) maps to Morse to reveal the flag.4 minMedium
Infrastructure
4 challenges · 40 pts- 10 ptsHealthy Hijack 1A filtered “safe command runner” in KPMG CTF 2026 Campus Edition that only allows network-debugging tools. Semicolon injection is neutralised and arguments are passed to the binary directly, but the validator only checks the first line, so a newline-separated second command slips past it and gives code execution as appuser, exposing the flag.3 minMedium
- 10 ptsLocks of Confusion 1A paper-trail infra challenge in KPMG CTF 2026 Campus Edition built on CVE-2008-0166, the Debian OpenSSL weak-PRNG bug. Follow an archive’s documentation to recover a legacy service account’s SSH public key, match it against the predictable weak keyset to recover its private key, then use that key’s own Base64 body as the password to an encrypted backup holding the flag.4 minMedium
- 10 ptsVaultDocs -1Reading a Debian box’s /etc/passwd through a Local File Inclusion bug in a document portal, spotting a leftover VirtualBox user, and logging in over SSH with its default password to grab the first flag in KPMG CTF 2026 Campus Edition.4 minMedium
- 10 ptsVaultDocs -2Escalating from the vboxuser login to root on the VaultDocs box by abusing a sudo NOPASSWD entry for /bin/tar and the GTFOBins file-read technique to retrieve /root/root.txt in KPMG CTF 2026 Campus Edition.4 minMedium
OSINT
3 challenges · 80 pts- 20 ptsA Clean TrailA multi-hop OSINT trail in KPMG CTF 2026 Campus Edition: read a carpet-cleaning van’s phone number off a Google Street View image to unlock a password-protected PrivateBin, follow the paste to a LinkedIn profile, find the target’s latest comment (Brainfuck code), and decode it to the flag.3 minMedium
- 30 ptsGolden HourA multi-hop OSINT trail in KPMG CTF 2026 Campus Edition: pivot from a photographer’s portfolio to her GitHub, pick the real LinkedIn out of two handles, decode leetspeak and Base64/Base32 breadcrumbs for a vault passphrase, geolocate a lighthouse photo to Peggy’s Cove, and pull the flag out of the full-res image’s EXIF.4 minMedium
- 30 ptsWestboundA 30-point multi-stage forensics chain in KPMG CTF 2026 Campus Edition: decode a phishing email into a screenshot, pull a hidden layer out of it with zsteg, rebuild files inlined in a 4 MB HTML page, read an AES key out of an audio spectrogram, recover an OpenSSL-encrypted git repo, and resurrect a deleted commit to find the real marker, while dodging three planted bait flags.6 minMedium
OT / IoT
2 challenges · 30 pts- 10 ptsBaud IntentionsWorking a simulated PLC’s locked UART maintenance shell in KPMG CTF 2026 Campus Edition: deriving the legacy service key from the device serial, authenticating, running the right diagnostic flags to unlock the maintenance/debug register range, and reassembling the flag from three debug buffers.3 minEasy
- 20 ptsLast WillAn OT/IoT MQTT challenge in KPMG CTF 2026 Campus Edition. A robots.txt-leaked /pub/ archive discloses a non-standard MQTT broker and two behaviours: the $-reserved namespace is skipped by wildcard subscribes, and duplicate client IDs evict the original client, firing its Last Will. Subscribing to $internal/# reveals the gateway’s client ID; stealing it triggers the Last Will message, which carries the Base64 flag.4 minMedium
Reverse Engineering
3 challenges · 70 pts- 10 ptsLogic BypassReversing a 64-bit ELF “auth” binary in KPMG CTF 2026 Campus Edition, ignoring the pile of decoy password-check functions, and recovering the flag directly from decode_flag, which just XORs a static ENC_FLAG array against an 8-byte repeating FLAG_KEY.4 minMedium
- 30 ptsAlgebraic NightmareAlgebraic Nightmare is a 30-point reversing challenge built around a bytecode VM whose 56-byte input check is buried under 14,000 Mixed Boolean-Arithmetic operations — “algebra wearing a disguise.” After decrypting the bytecode and pruning dead nodes (only 662 of 14,000 matter), the obfuscation collapses into a small 3-round invertible hash over seven 64-bit words. Because every step is reversible, you can run it backwards from the target constants to recover the flag — no solver needed, though z3 cracks it in ~13 seconds too.7 minHard
- 30 ptsMatrix ReloadA menu-based binary with a dangling-pointer bug: free a user, reclaim its heap chunk via “create data,” overwrite its function pointer with a hidden reveal_flag, and trigger it to leak the flag — a textbook tcache Use-After-Free.7 minMedium