Threat Intelligence
Attacker tradecraft, delivery techniques and the campaigns behind them.
RedEcho and the China-Nexus Targeting of India's Power Grid
Not every threat to India is fraud or Pakistan-nexus espionage. China-linked intrusion sets have repeatedly targeted India's power sector and critical infrastructure using ShadowPad and compromised internet-facing devices. A profile of RedEcho, TAG-38 and what it means for OT defenders.
- Sep 182026Sep 18, 2026
SideCopy: The APT36-Aligned Group That Copies SideWinder
A profile of the Pakistan-nexus group that mimics another actor's tradecraft to confuse attribution, overlaps with Transparent Tribe, and has pushed from Indian government and defence into research and academia with ActionRAT, AllaKore and ZIP-plus-LNK delivery.
3 min#apt#india#sidecopy
- Sep 102026Sep 10, 2026
Transparent Tribe (APT36): The Persistent Threat to Indian Government and Defence
A profile of the Pakistan-nexus espionage group that has spent a decade targeting Indian government, military and education, with Crimson RAT, CapraRAT on Android, and an ever-shifting set of lures. Who they are, how they operate, and what to watch for.
3 min#apt#india#apt36
- Jul 22026Jul 2, 2026
The APK Is the Exploit: How India's Fake-Challan Scam Became an Industry
There is no zero-day here. The attacker's whole chain is one Android app the victim installs by hand, after a WhatsApp message about a traffic fine or a gas bill. A June 2026 arrest in Gujarat showed it has become a supply chain, with a Telegram storefront and roughly 400 buyers. Here is how it works.
7 min#android#india#smishing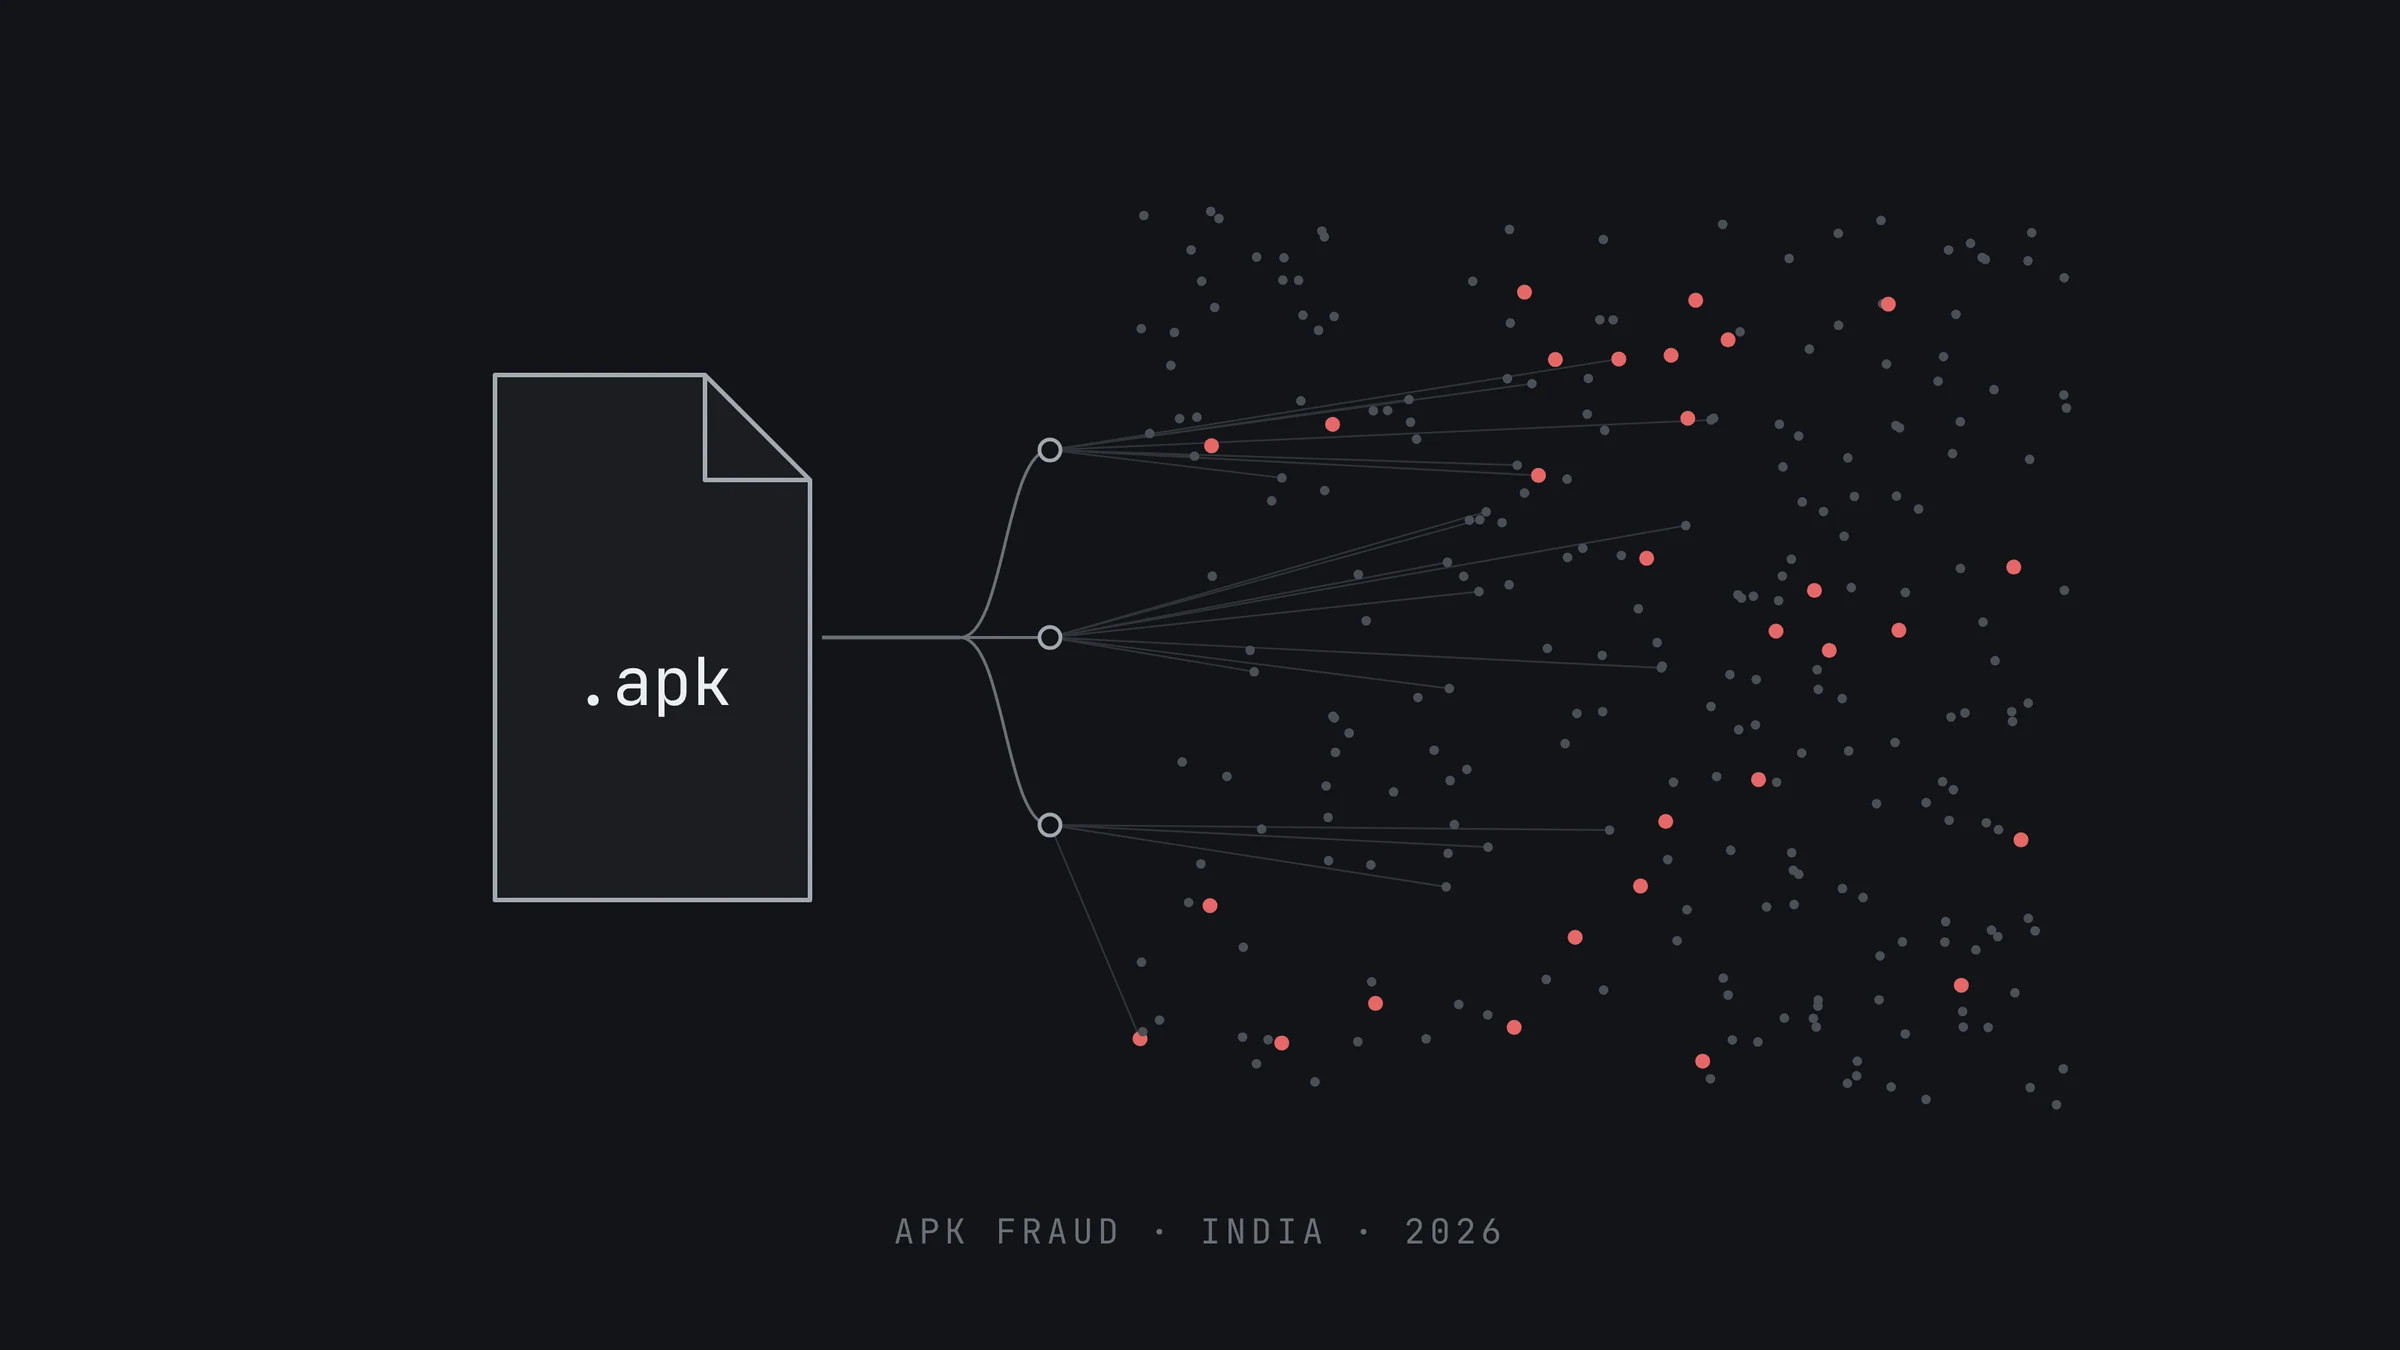
- Apr 142026Apr 14, 2026
FrostArmada: How APT28 Turned Old Home Routers Into a Microsoft 365 Interception Network
Russia's GRU didn't need malware on anyone's laptop. It changed one DNS setting on thousands of neglected TP-Link and MikroTik routers, then waited for the right people to click past a certificate warning. Here is how the FrostArmada campaign worked, why MFA didn't stop it, and what to check.
7 min#apt28#dns-hijacking#aitm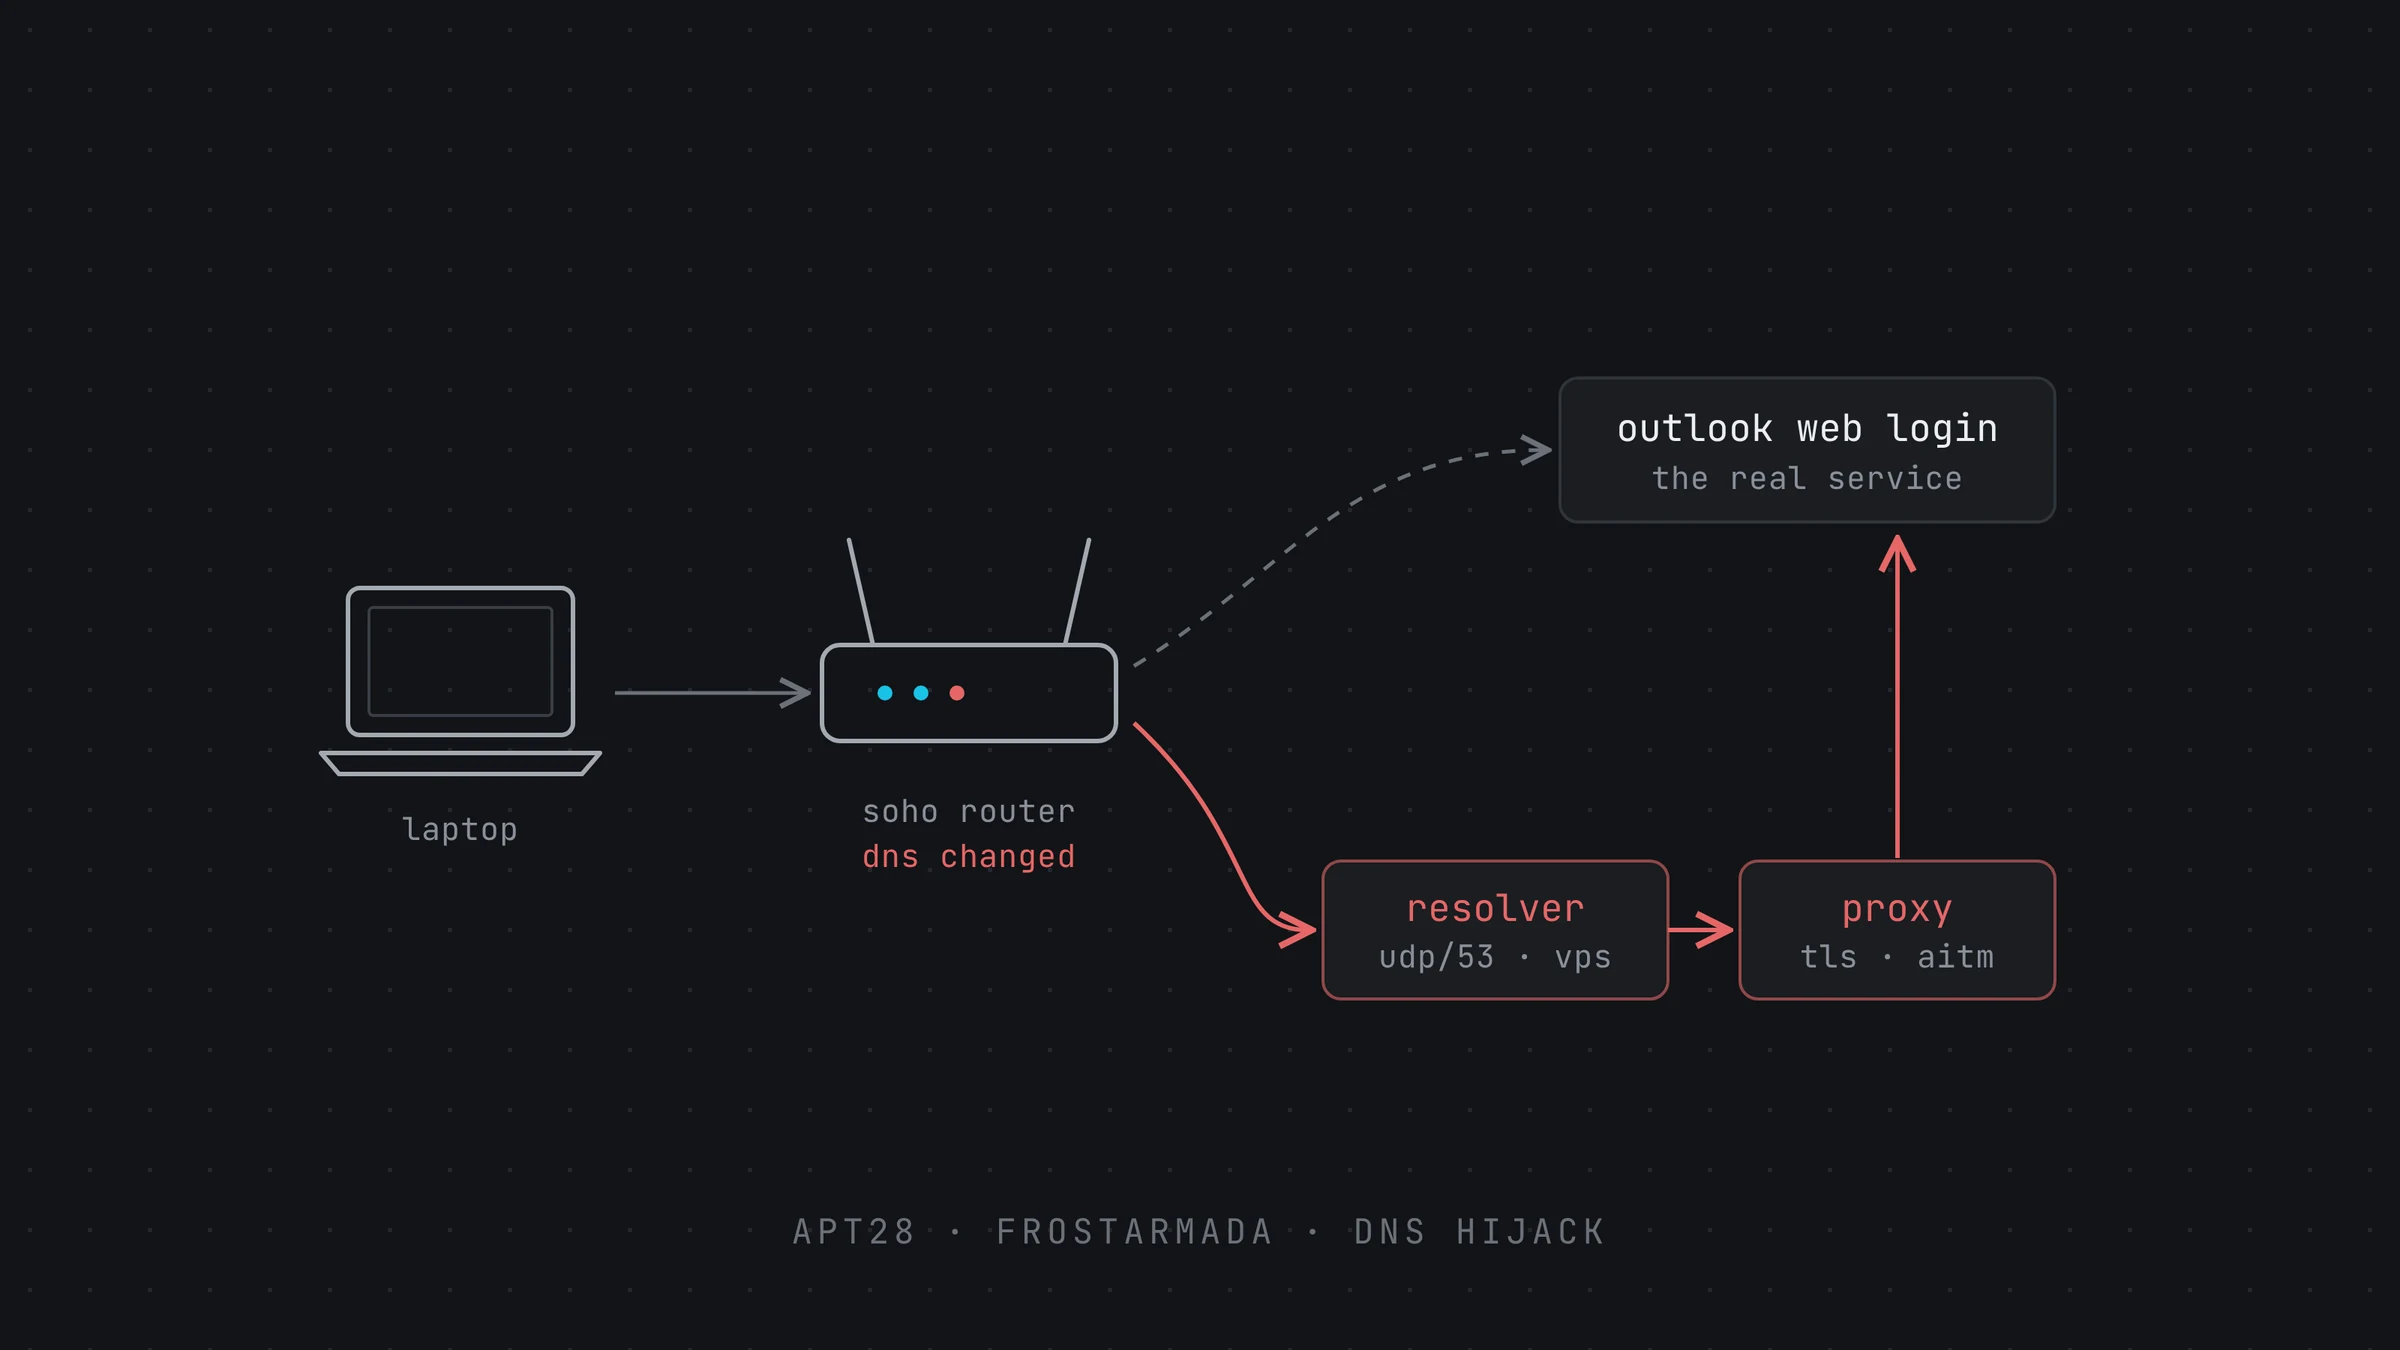
- Mar 12026Mar 1, 2026
How Attackers Use WebDAV to Deliver Malware Without Browser Warnings
Why malware no longer needs your web browser to breach your network-and how attackers are weaponizing legacy WebDAV protocols.
7 min#initial-access#phishing#windows
- Feb 82026Feb 8, 2026
The Invisible Siege: Why Modern APTs Have Weaponized the Operating System
The era of "smash-and-grab" malware attacks is fading among state-sponsored actors. Today’s Advanced Persistent Threats (APTs) have shifted toward a "Living-off-the-Land" (LotL) paradigm.
5 min#apt#lotl