Malware Analysis
Hands-on static and dynamic analysis of malware samples, from initial infection to C2, with indicators of compromise.
Hiding in Plain Sight: Deconstructing the UPSTYLE Backdoor (CVE-2024-3400)
A technical deep dive into the UPSTYLE malware and the CVE-2024-3400 vulnerability. This analysis dissects the malware's three-stage Python payload, its novel "living-off-the-land" C2 communication, and provides actionable IOCs for defenders.
- Dec 132025Dec 13, 2025
Inside the RTO-Challan Dropper: Anatomy of a Two-Stage Android Bank Stealer
A fake e-Challan app that installs a second, hidden app, harvests Aadhaar, PAN and full card and UPI details through counterfeit payment screens, intercepts every incoming SMS, and hides its traffic behind a VPN service. A technical walk through CYFIRMA's analysis.
4 min#android#india#rto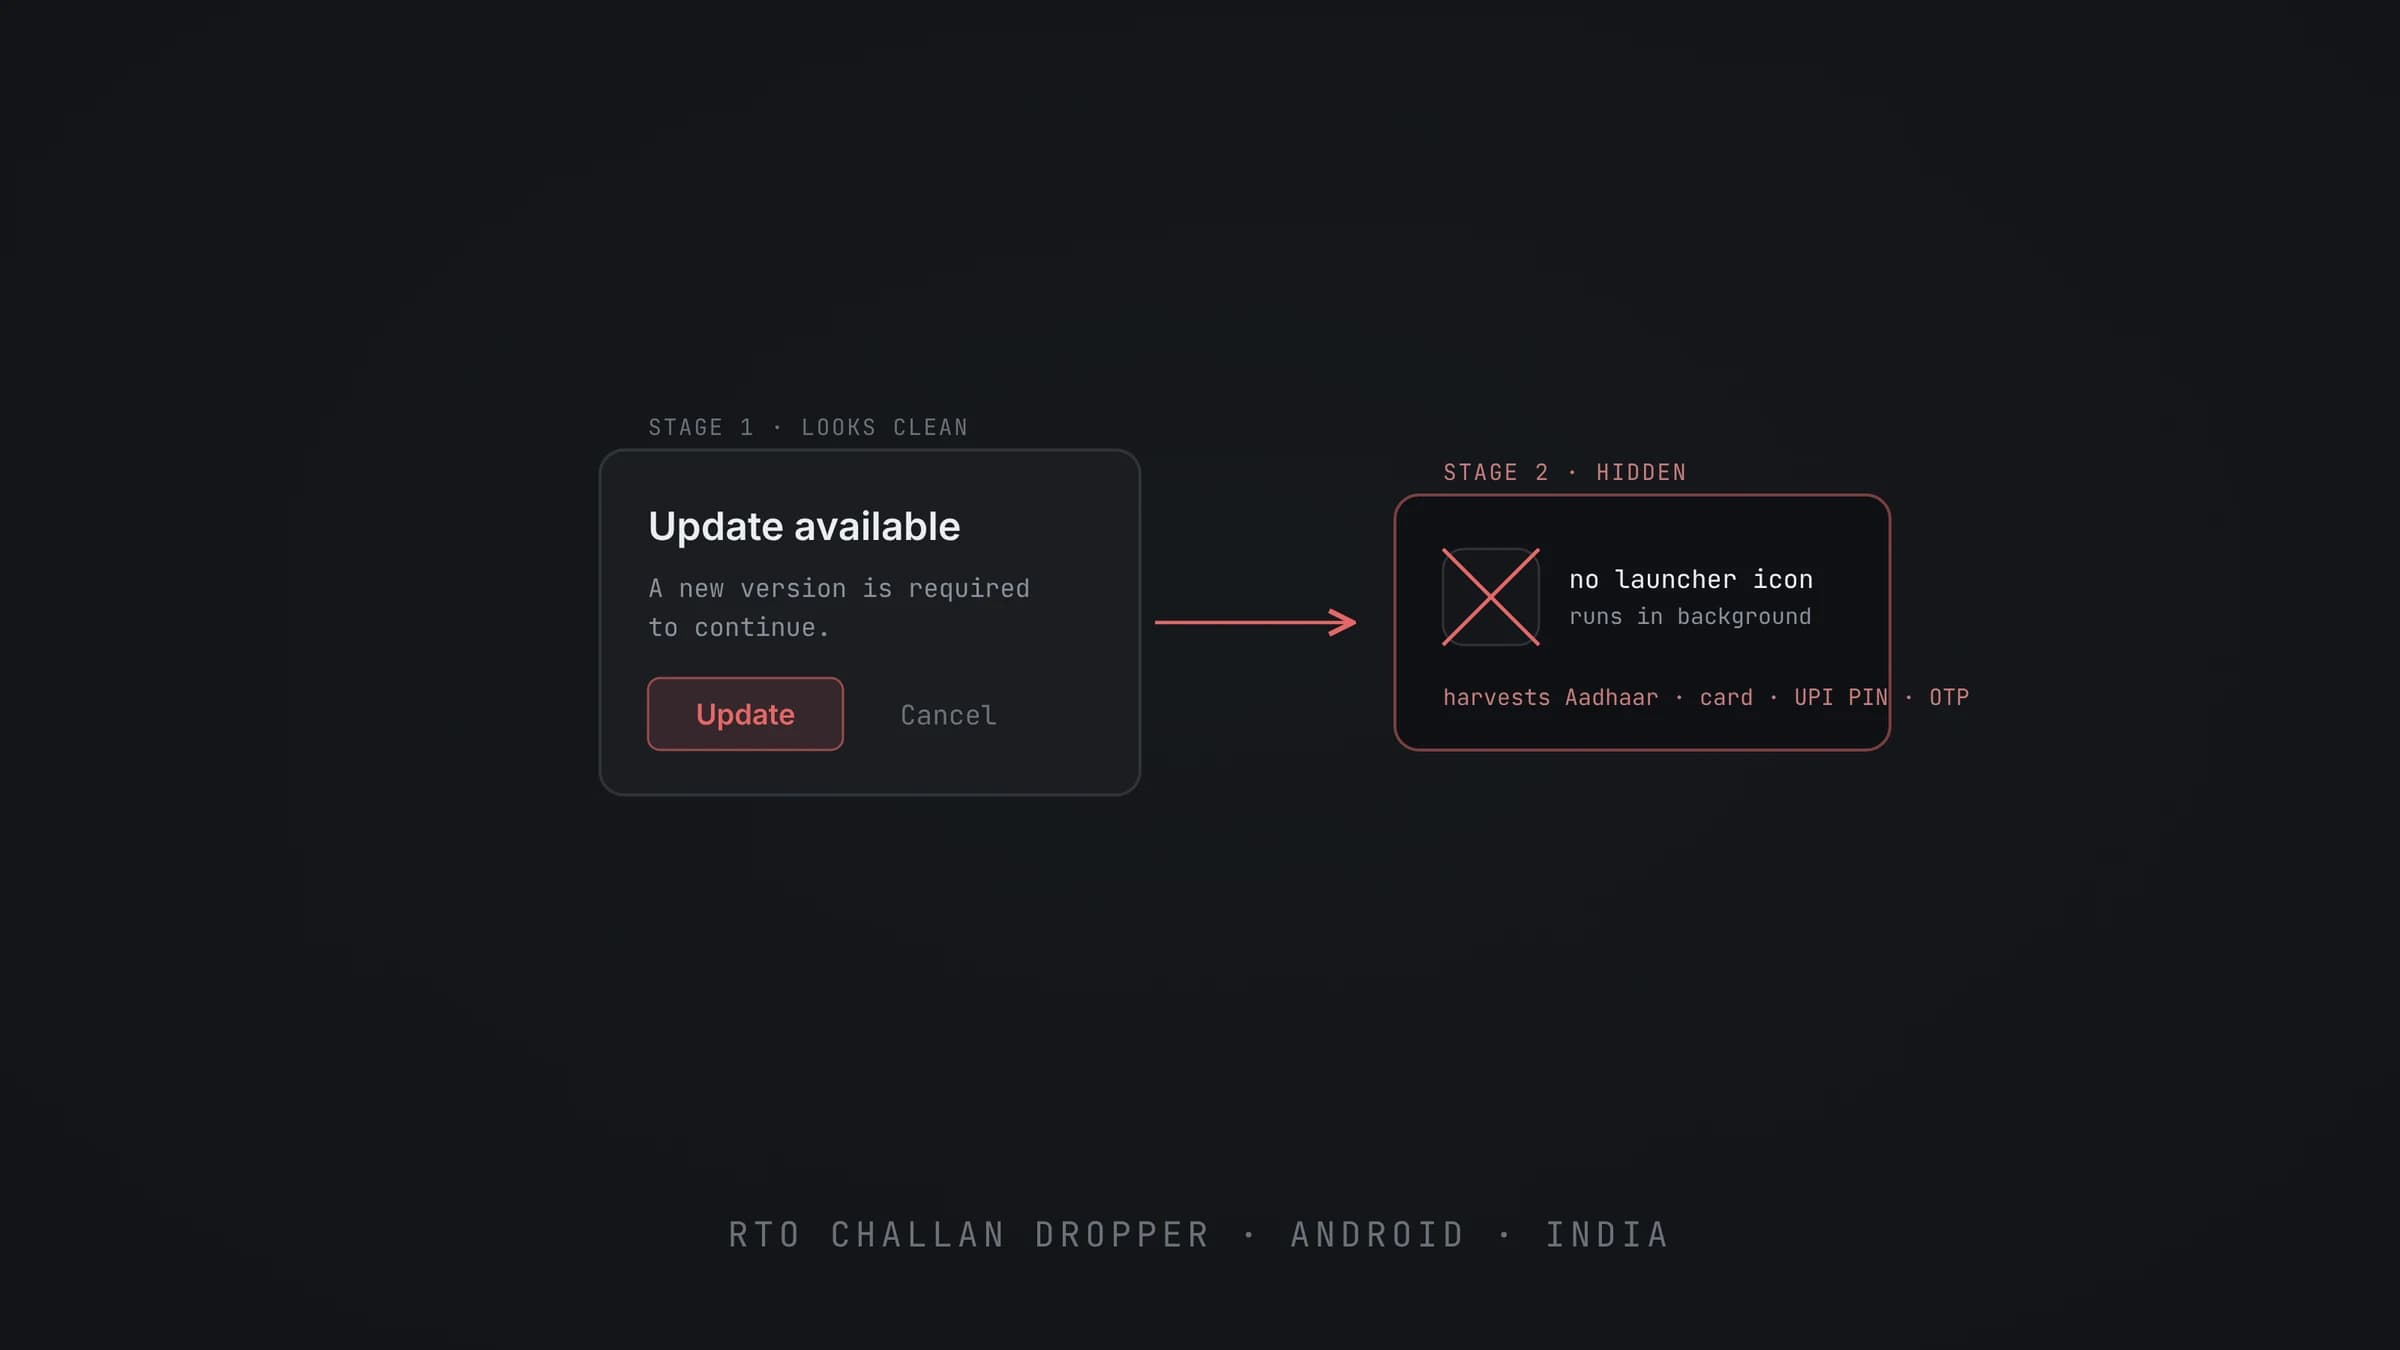
- Oct 222025Oct 22, 2025
Deconstructing a Stealthy Android Trojan: A Case Study in Phishing and Evasion
From a compromised WhatsApp group to a Man-in-the-Middle attack, this is the story of how a sophisticated Android malware uses deception and advanced anti-analysis techniques to steal banking credentials.
4 min#android#phishing#mobile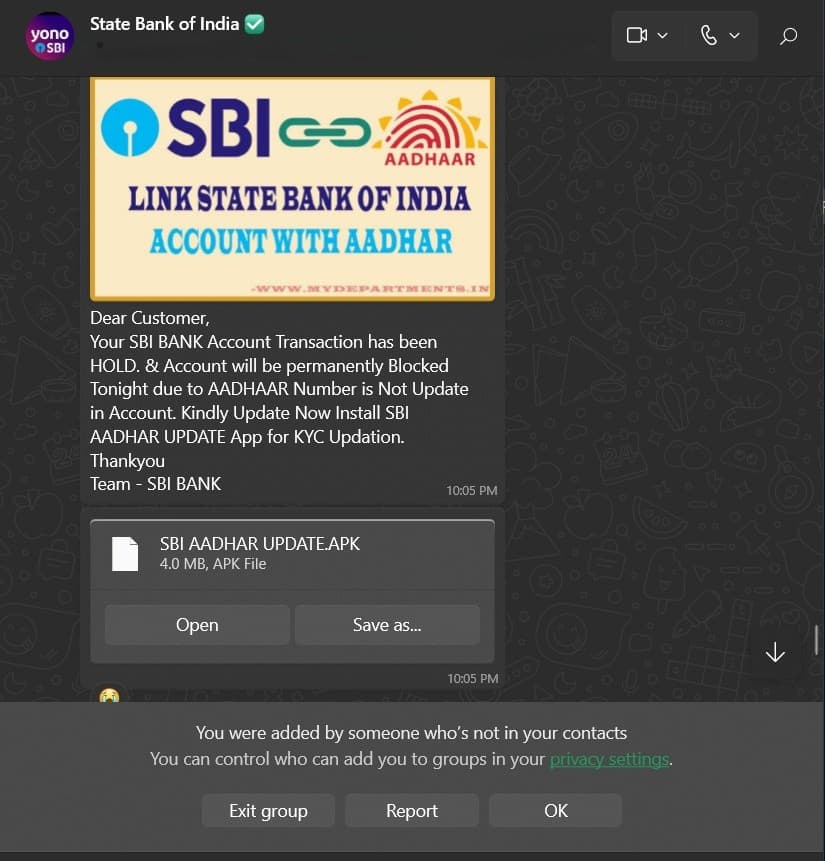
- Oct 202025Oct 20, 2025
GhostBat RAT: How RTO-Themed Android Malware Steals Your UPI PIN
A multi-stage Android RAT that poses as the mParivahan RTO app, spreads over WhatsApp, and drains accounts through a fake UPI payment flow. It hides on GitHub, talks to a Telegram bot, and even mines crypto on the side. Here's how it works and what to watch for.
4 min#android#india#rto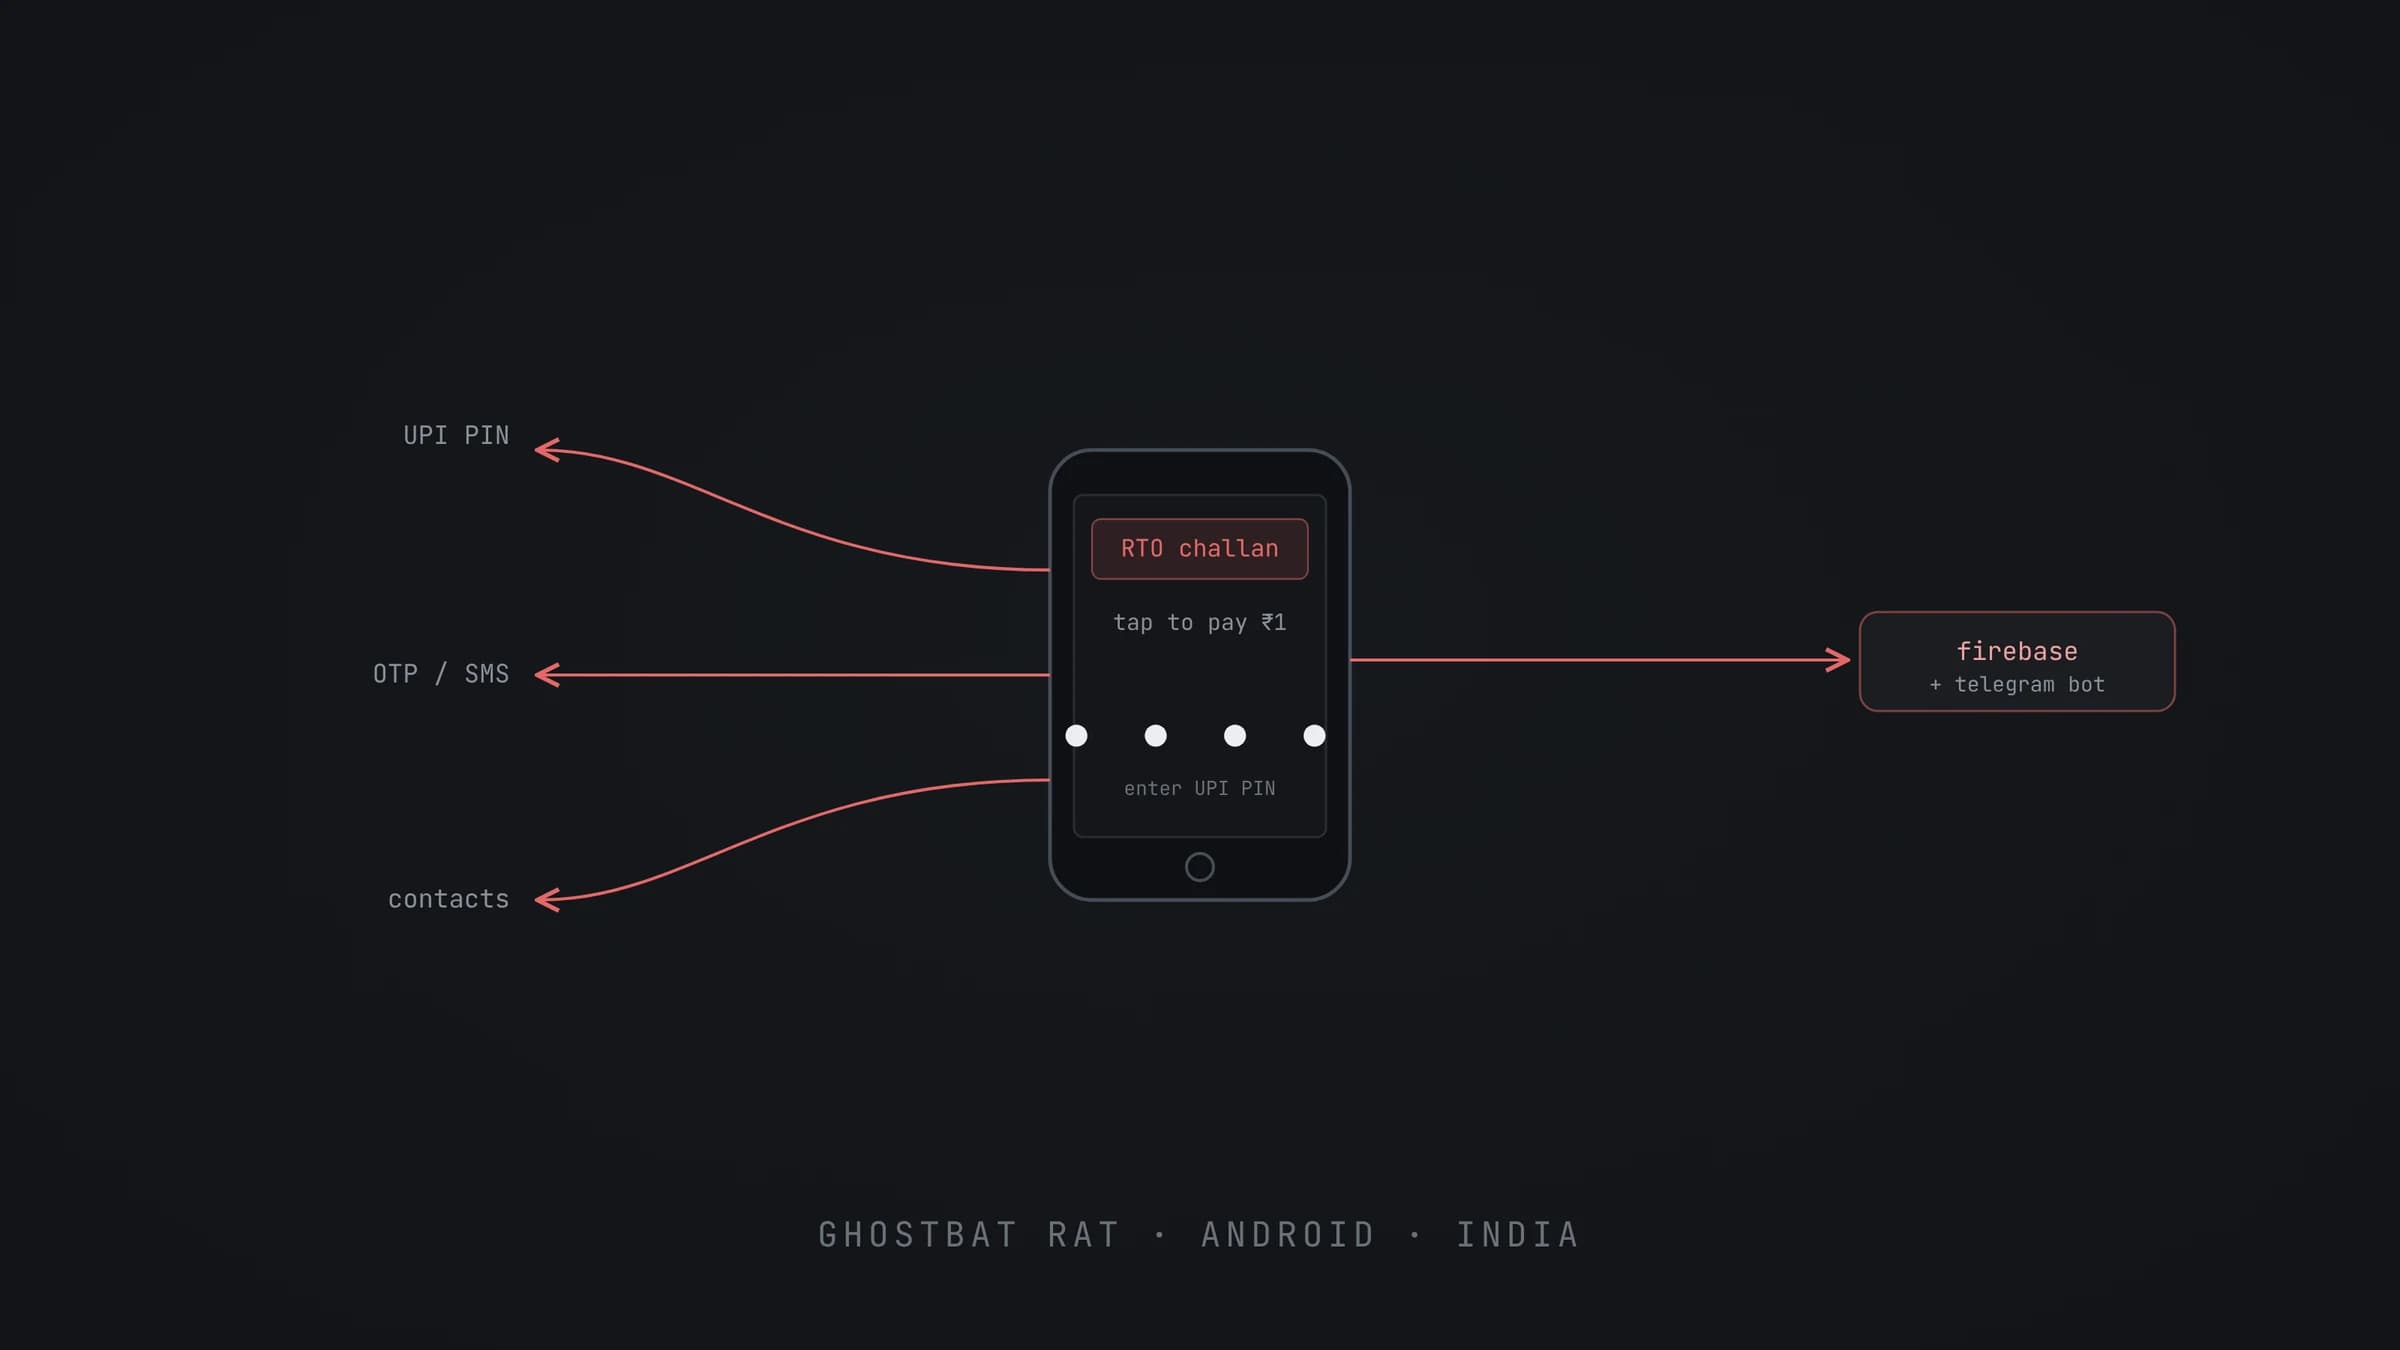
- Sep 22025Sep 2, 2025
How Risen Ransomware Works: An IDA Pro Deep Dive
A step-by-step static analysis of the Risen ransomware, uncovering its evasion tactics, persistence mechanisms, and key indicators of compromise from a LetsDefend challenge.
4 min#ransomware#reverse-engineering#letsdefend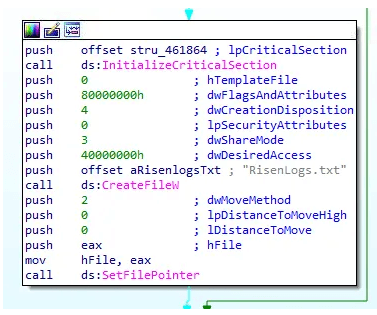
- Aug 262025Aug 26, 2025
Deconstructing IcedID: A Hands-On Walkthrough of a Modern Malware Attack
From a malicious Word document to C2 communication, this is a step-by-step analysis of the LetsDefend IcedID challenge, revealing the tools and techniques used to dissect a notorious banking trojan.
5 min#loader#maldoc#letsdefend