The App Frontier - (Cortex Cloud) - Writeup
On this page
- 1.Challenge Overview
- 2.Answer Ledger
- 3.The Path to Production
- 4.Q1: Riskiest Asset Across The Entire Business Application
- 5.Q2: Tracing The CI/CD Pipeline To Its Running Instance
- 6.Q3: Identifying And Triaging CVEs In Core Images
- 7.Q4: Leveraging Playbooks To Update Configuration
- 8.Q5: Leveraging Pull Requests To Fix Configuration
- 9.Q6: Finding The Line That Leaks The Token
- 10.Q7: Prioritizing Identity Risk
- 11.Takeaways
Challenge Overview
| Event | Palo Alto Networks Cortex CTF 2026 |
|---|---|
| Scenario | The App Frontier: Securing an Application from Code to Cloud to SOC |
| Platform | Cortex Cloud |
| Questions | 7 (5 pts each) |
| Points | 35 |
| App | Business application Finance-app |
Finance-App spans a GitHub repository, a GitHub Actions pipeline, container images in ECR, an EKS cluster and an EC2 node in AWS. The questions trace where the path to production went wrong, from the riskiest asset back to a leaked key in Terraform and forward to the pull request that fixes the template.
Answer Ledger
| Q | Challenge | Answer |
|---|---|---|
| 1 | Riskiest Asset Across The Business Application | aws-proserve-java-app-dev |
| 2 | Tracing The CI/CD Pipeline To Its Instance | https://api.github.com/users/nishantorg3433 |
| 3 | Identifying And Triaging CVEs In Core Images | CVE-2020-17530 |
| 4 | Leveraging Playbooks To Update Configuration | aws-ec2-instance-metadata-options-modify |
| 5 | Leveraging Pull Requests To Fix Configuration | https://github.com/nishantorg3433/finance-app-code/pull/5 |
| 6 | Finding The Line That Leaks The Token | 46 |
| 7 | Prioritizing Identity Risk | runtime-EKSNodeGroupRole |
The Path to Production
| Stage | Asset |
|---|---|
| Code | GitHub repository nishantorg3433/finance-app-code, with Terraform under tools-iac/ and CloudFormation under iac/ |
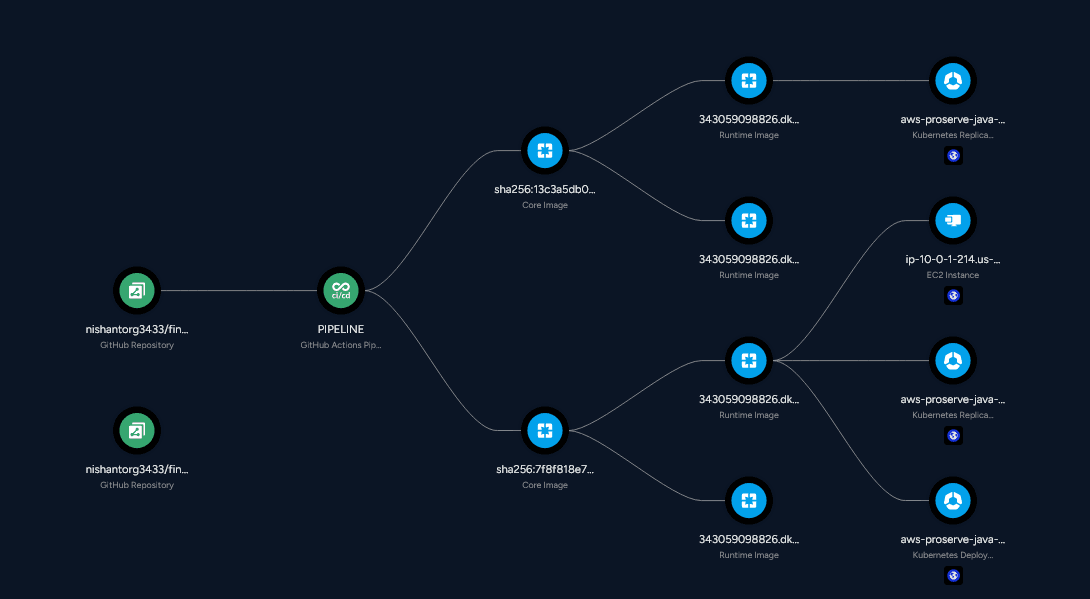
| Build | A GitHub Actions pipeline builds two core images, sha256:13c3a5db0… and sha256:7f8f818e7… |
| Registry | Runtime images in 343059098826.dkr.ecr.us-east-1.amazonaws.com/code2cloud-ecr |
| Runtime | EKS cluster pc-national-bank-kubecon (us-west-1) runs aws-proserve-java-app-dev on EC2 node ip-10-0-1-214 |
| Identity | The node carries runtime-EKSNodeGroupRole, with administrative access |
Q1: Riskiest Asset Across The Entire Business Application
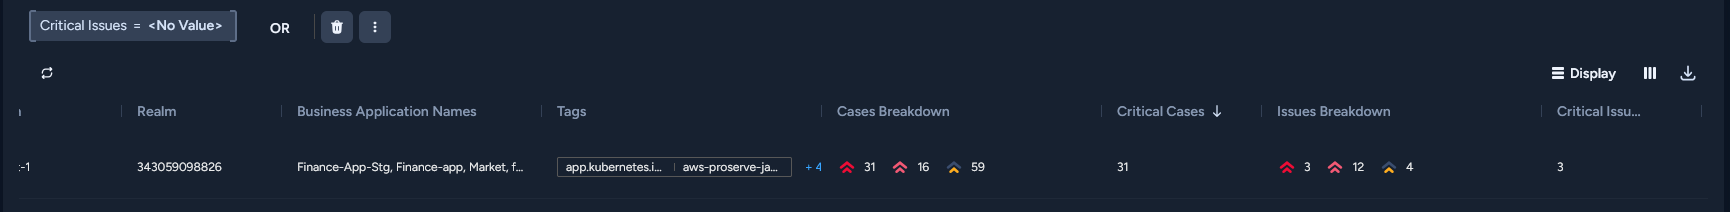
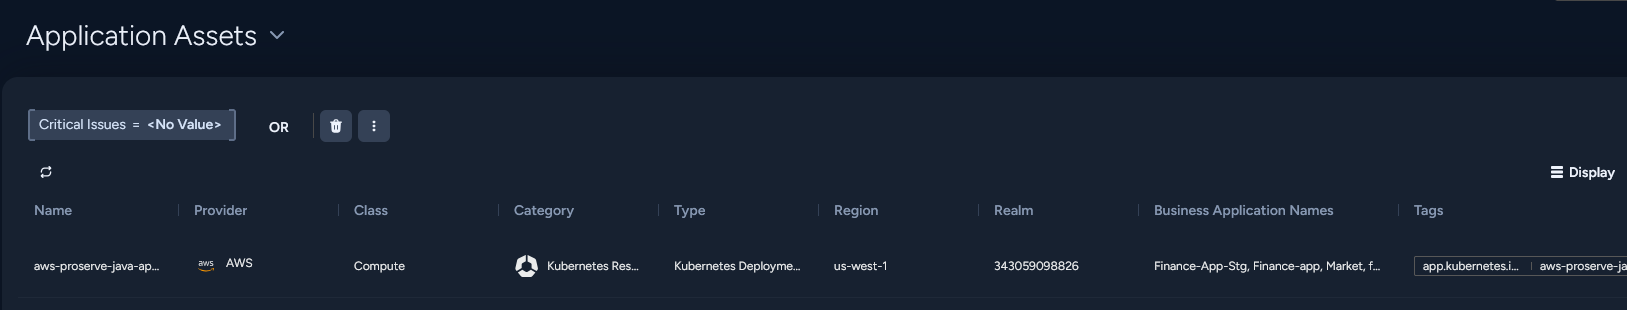
The Issues list is the wrong starting point. Open the Finance-app business application, go to Topology → Inventory → Application Assets, add the Critical Cases column if needed, and sort it descending.
Flag: aws-proserve-java-app-dev
Q2: Tracing The CI/CD Pipeline To Its Running Instance
The Application Assets table only holds runtime assets, so the pipeline does not appear there, and the "CI/CD Pipeline Build URL" column stays empty. Switch Topology to Graph and follow the chain from left to right.
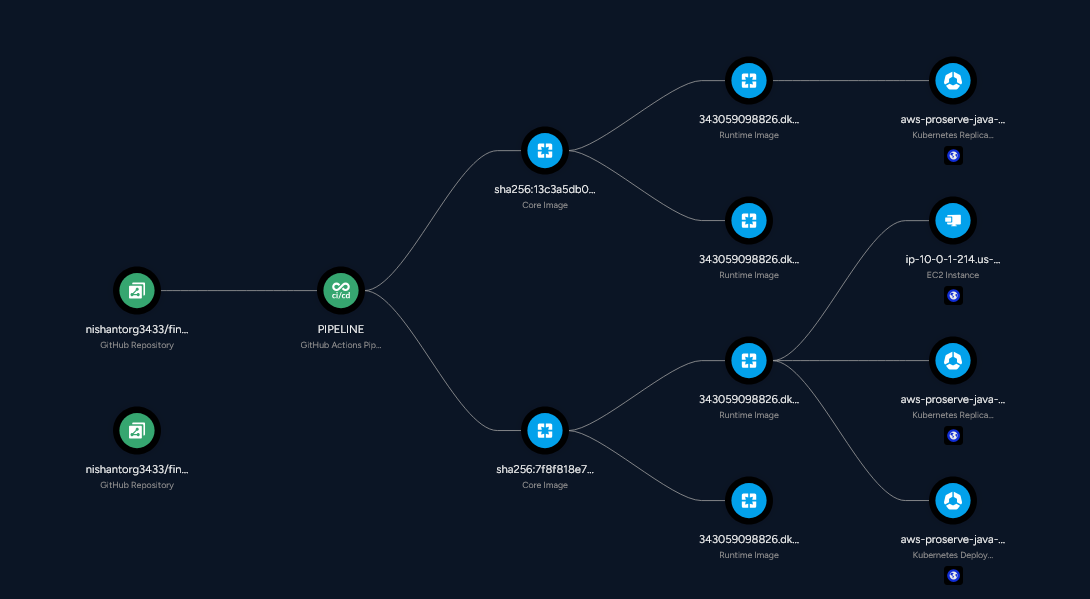
Clicking the pipeline leads to its GitHub Actions CI Instance, nishantorg3433, whose properties include the Instance URL.
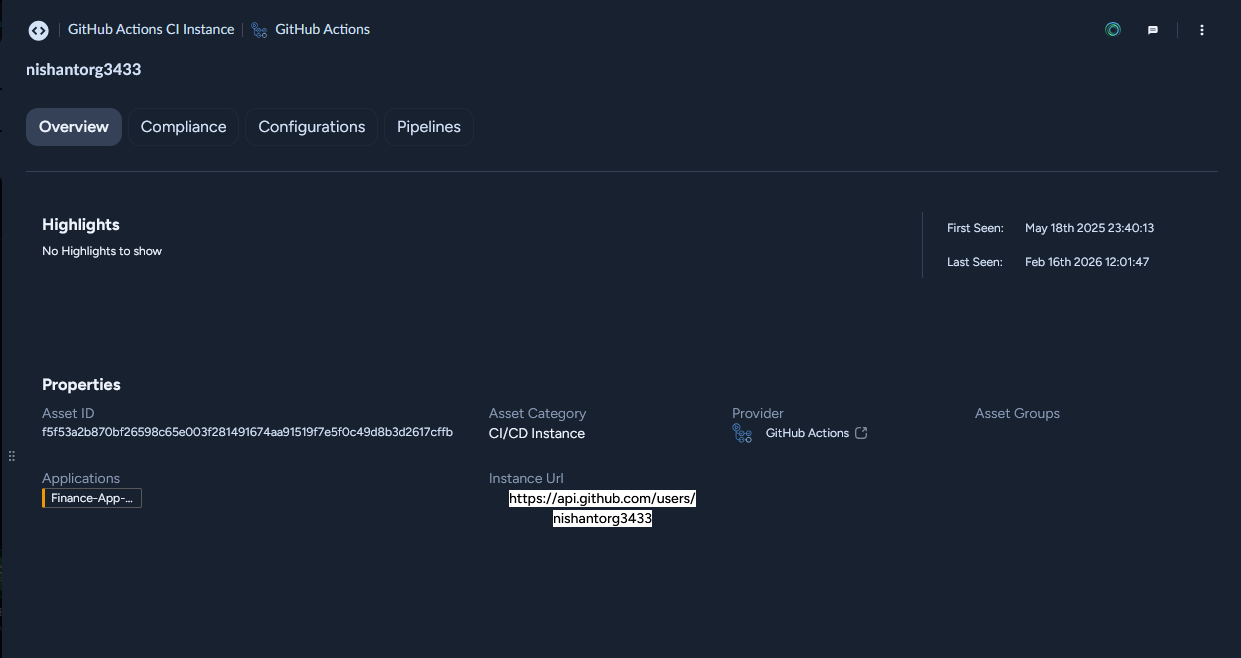
Flag: https://api.github.com/users/nishantorg3433
Q3: Identifying And Triaging CVEs In Core Images
From the graph, open each core image and its Vulnerabilities tab. The two lists are identical, so every CVE is shared. The one to remediate first is the only CVE with a perfect CVRS score.
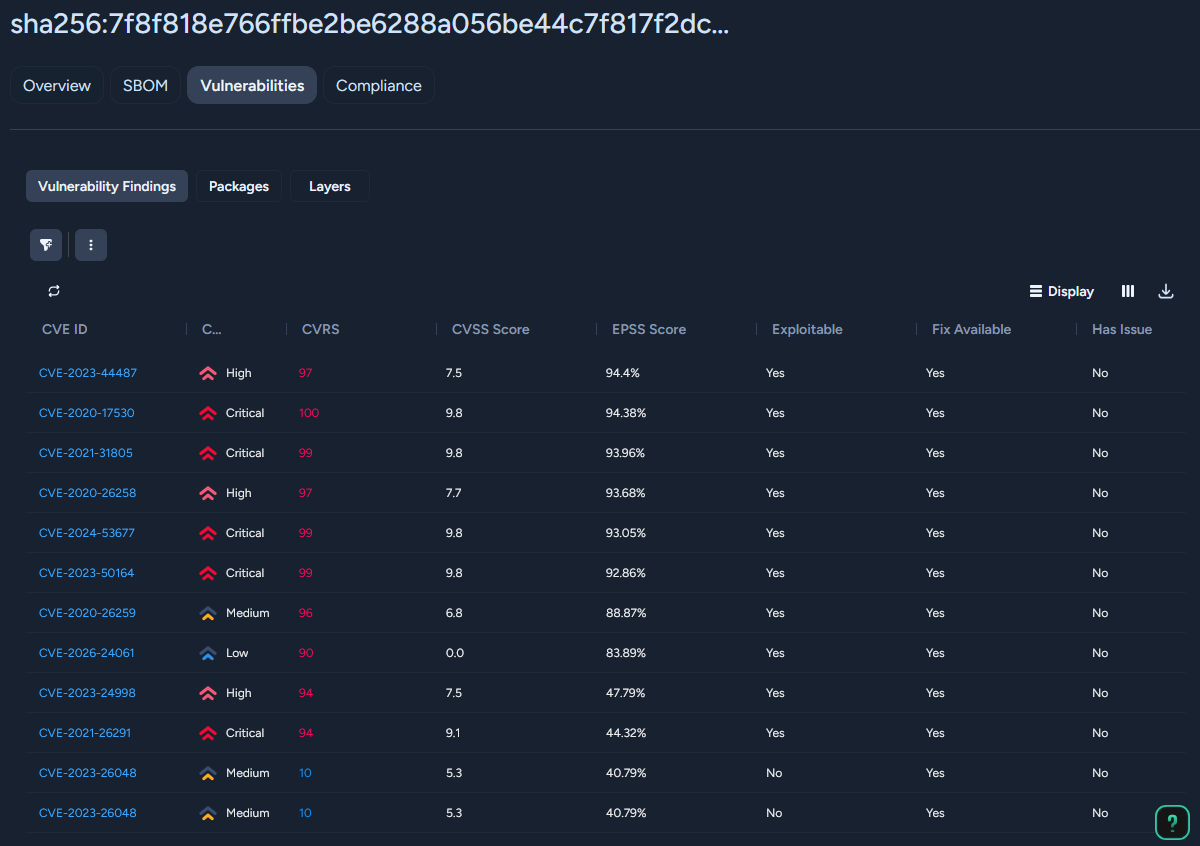
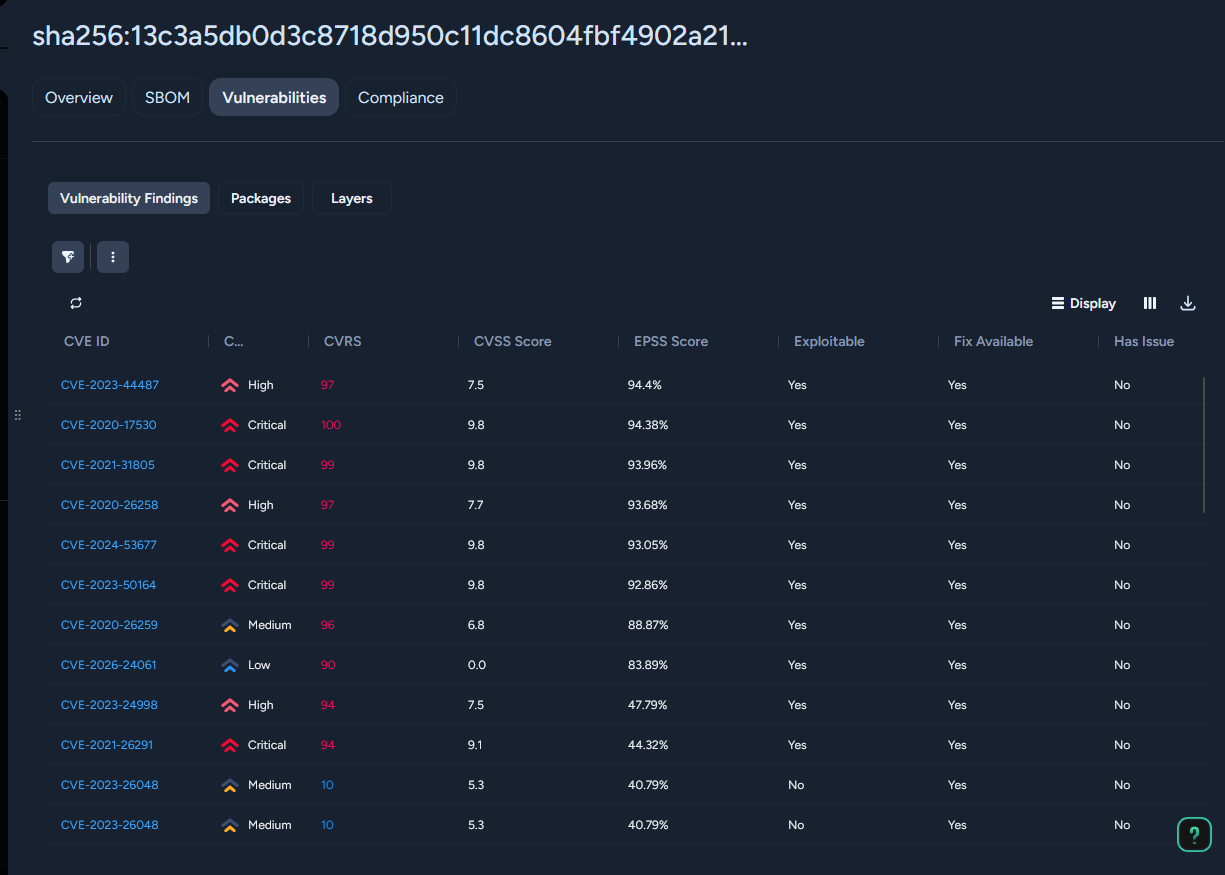
CVE-2020-17530 has CVRS 100, CVSS 9.8 and EPSS 94.38%, and is exploitable with a fix available. It is the Apache Struts 2 OGNL injection flaw that allows remote code execution, which matters for a Java application.
Flag: CVE-2020-17530
Q4: Leveraging Playbooks To Update Configuration
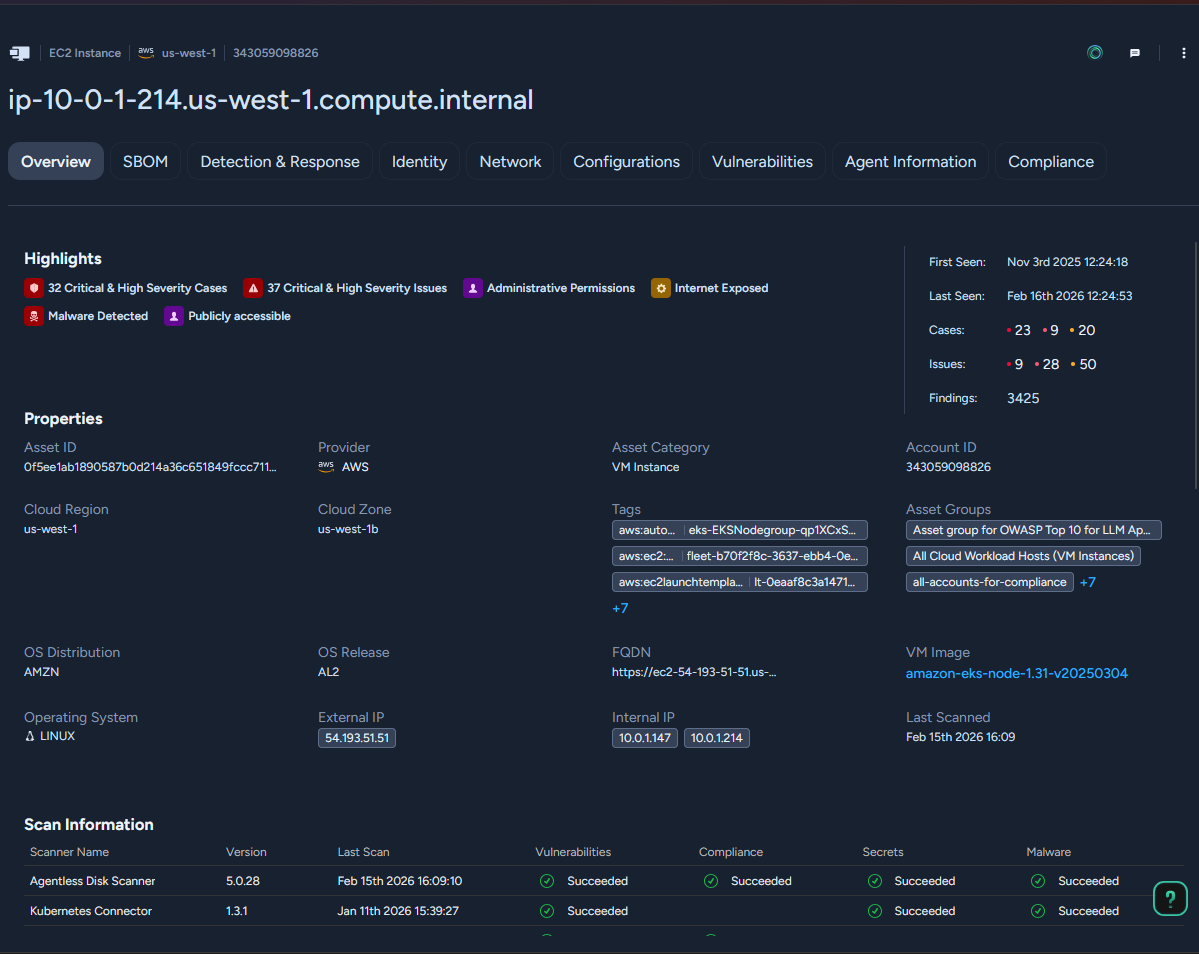
Finance-App's only EC2 instance is ip-10-0-1-214.us-west-1.compute.internal, an EKS worker node with an external IP, administrative permissions and malware detected.
The asset page does not show remediation history. That lives on the CSPM issue #492849, "AWS EC2 instance not configured with Instance Metadata Service v2 (IMDSv2)". Its War Room logs the playbook run: task #23, "Update AWS EC2 Instance Metadata Service", calls the metadata-options script with http_tokens="required" on i-09d5ae3daed9eac4c, and the next task prints "Remediation - Success".
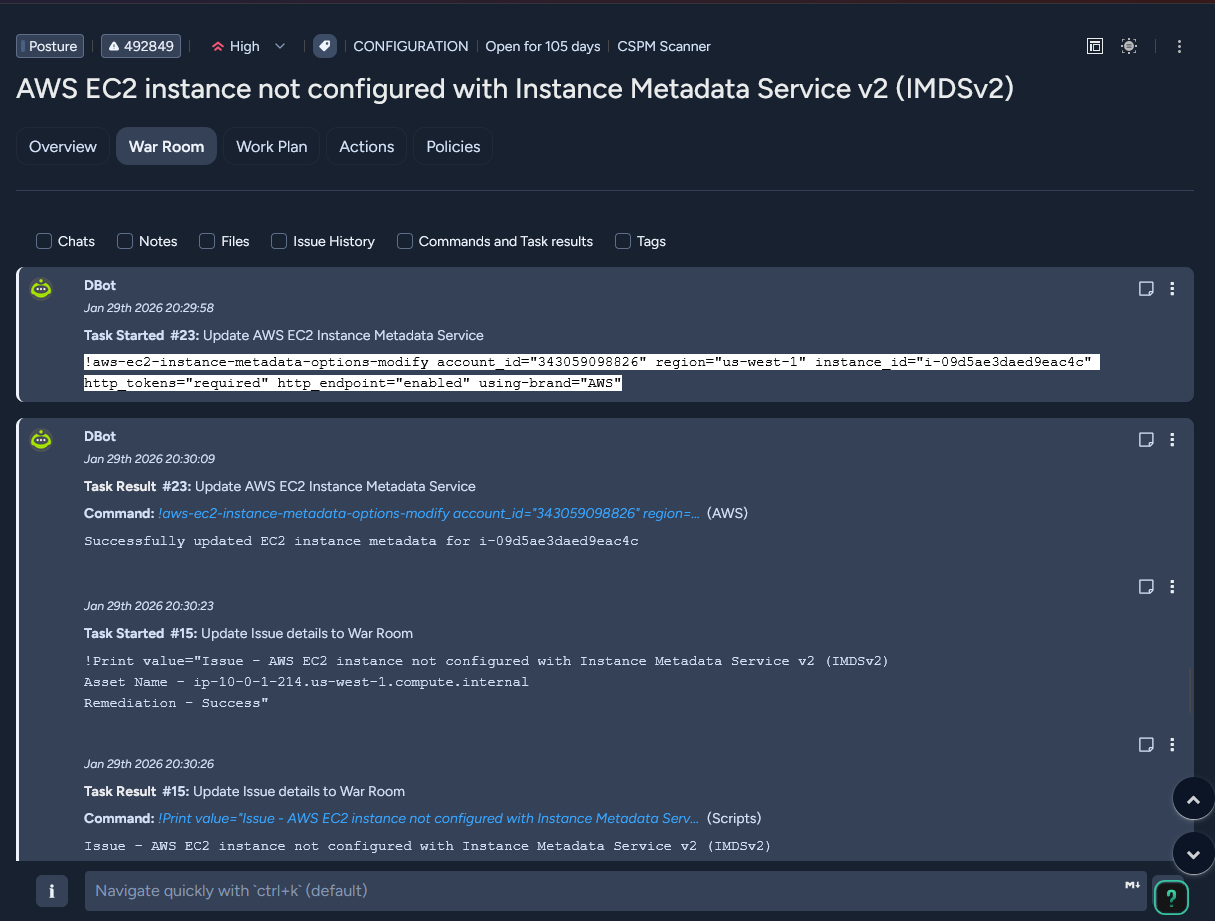
The question asks for the script or task name, not the full command, so drop the ! and every argument.
Flag: aws-ec2-instance-metadata-options-modify
Q5: Leveraging Pull Requests To Fix Configuration
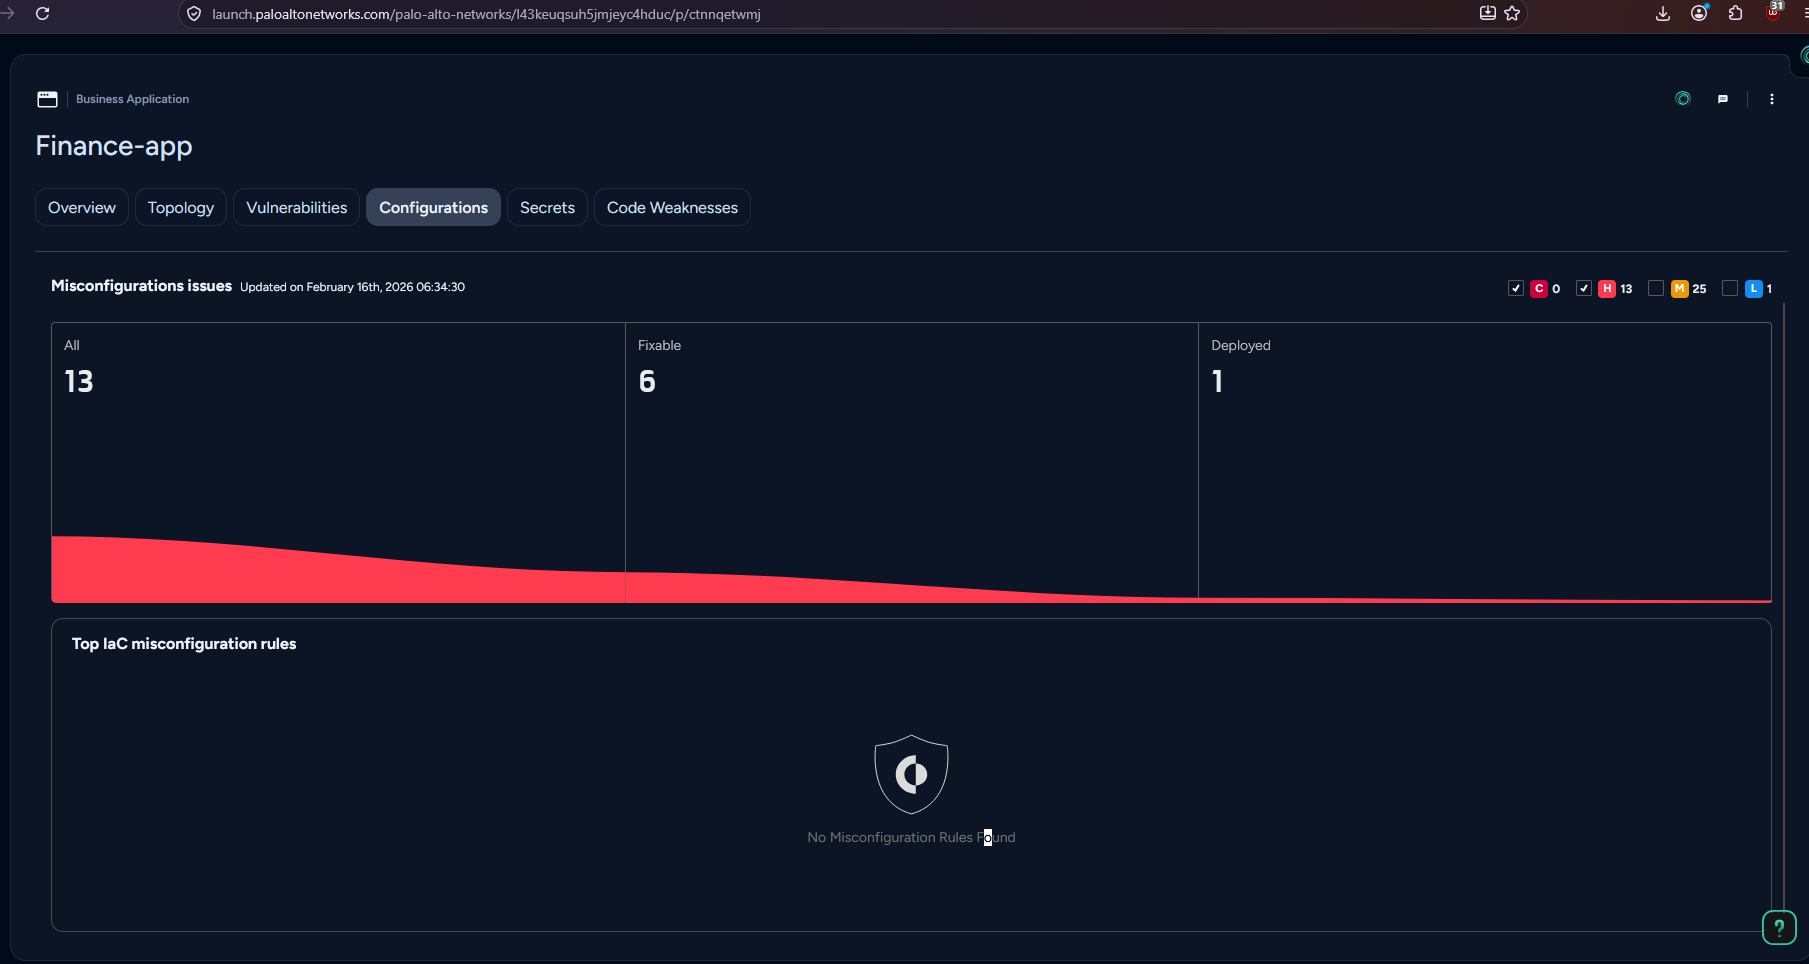
Finance-app's Configurations tab summarises 13 misconfigurations, 6 of them fixable. Clicking the Fixable tile opens those six issues.
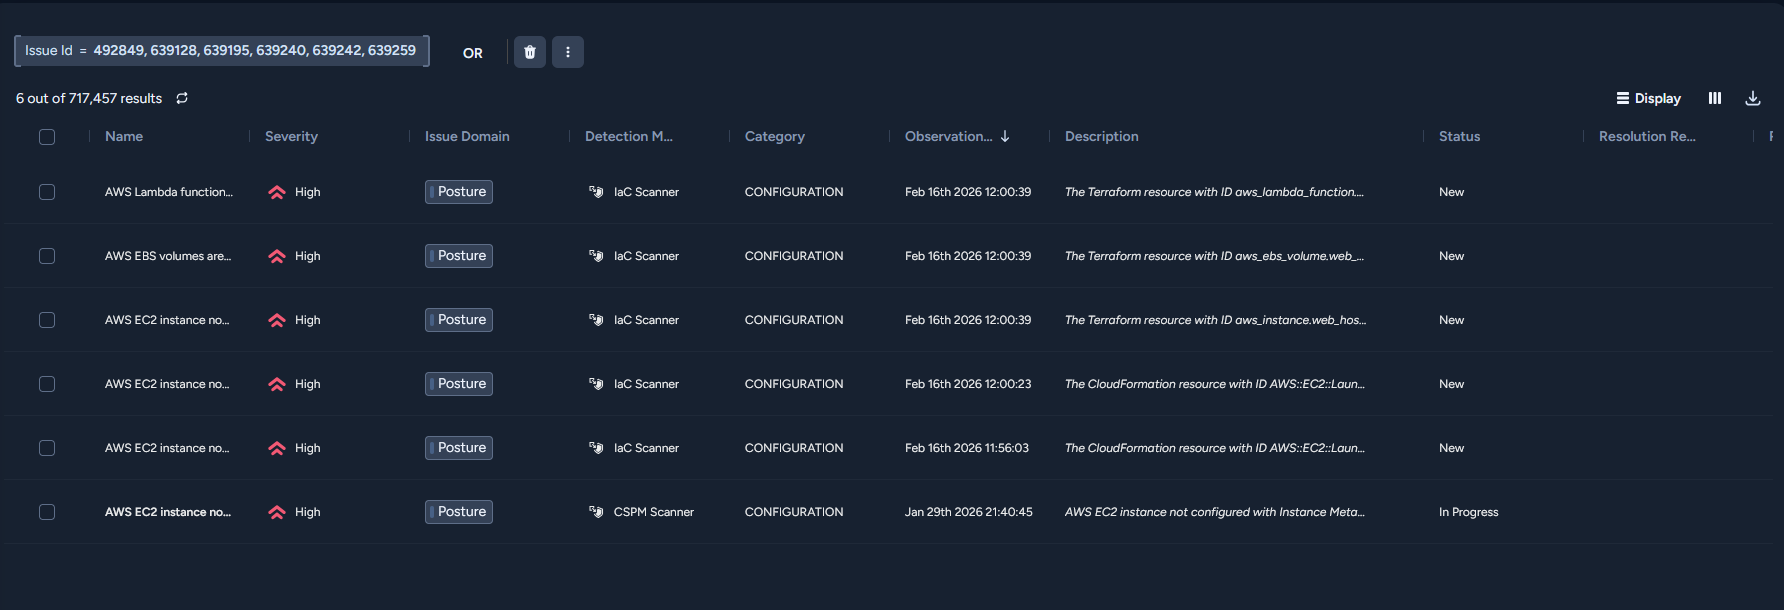
The Terraform issue on ec2.tf had no PR, and trying to open one failed. The CloudFormation issue #639195, on the EKSNodegroupTemplate launch template in finance-app-code/iac/lab-cft.json, already had one: its Actions tab reads "Issue is pending to be fixed as part of" the PR.
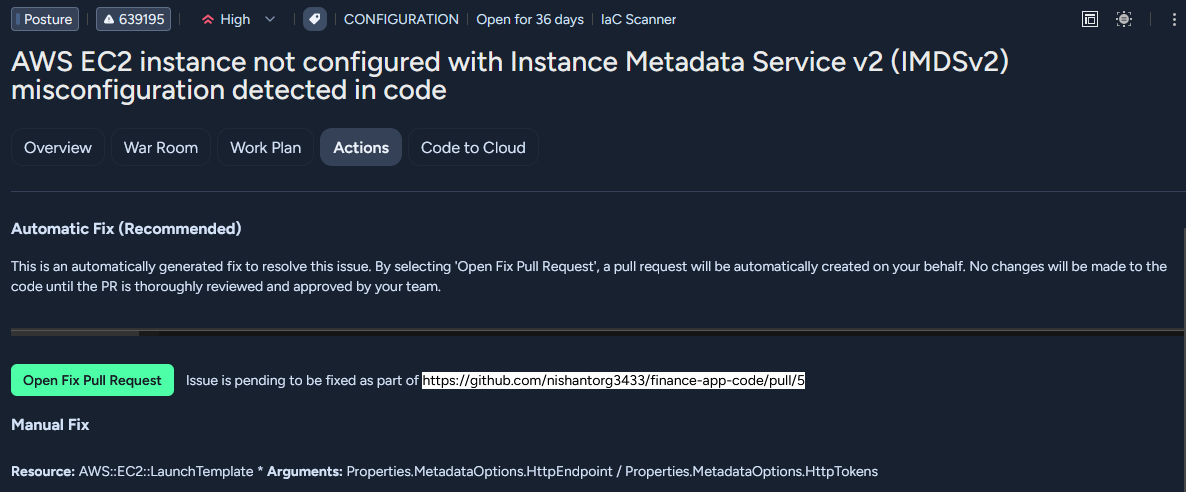
An issue that already has a PR shows the link next to the Open Fix Pull Request button. Check every matching issue before creating a new PR in a shared lab.
Flag: https://github.com/nishantorg3433/finance-app-code/pull/5
Q6: Finding The Line That Leaks The Token
Finance-app's Secrets tab lists secrets found in the deployed repository. The AWS access token finding on the Lambda Terraform file points to the exact line in its GitHub evidence.
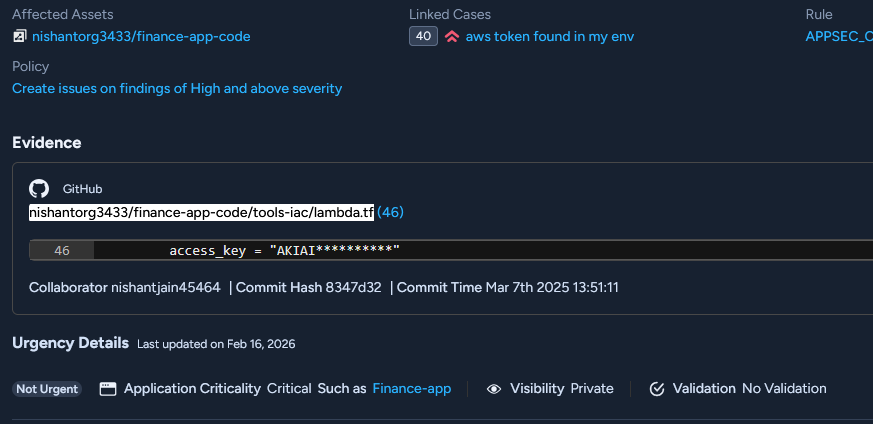
The key sits at tools-iac/lambda.tf line 46 as access_key = "AKIAI…", committed by nishantjain45464 in commit 8347d32.
Flag: 46
Q7: Prioritizing Identity Risk
The Kubernetes replicas have a limited attack surface, but the standalone EC2 node does not. On ip-10-0-1-214, the Identity tab lists one attached IAM role.
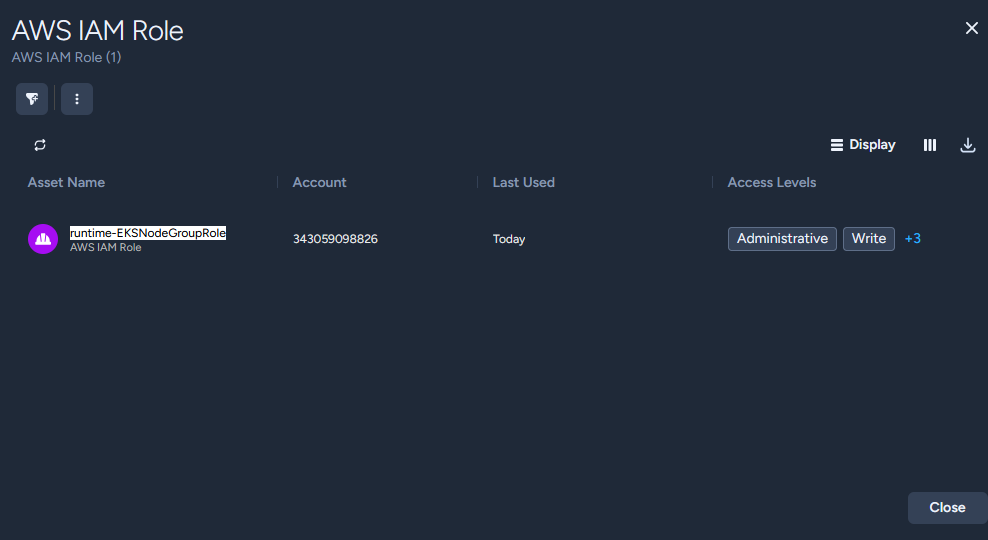
An attacker who reaches this exposed node, and before the Q4 fix could read its credentials over IMDSv1, inherits administrative access to the account.
Flag: runtime-EKSNodeGroupRole
Takeaways
- The business application view is the way into multi-platform questions. It ties repos, pipelines, images and cloud assets into one inventory and one graph.
- Tables show assets; graphs show relationships. The pipeline and CI instance only appear when you walk the Topology graph.
- Fix vulnerabilities at the core image. One CVE in a base image reaches every runtime image built from it.
- Runtime and code remediation are separate. The playbook fixed the running node; the pull request fixes the template that would redeploy IMDSv1.
- A hard-coded access key in IaC and an admin node role are each a path to account takeover. Rotate the key and scope the role.